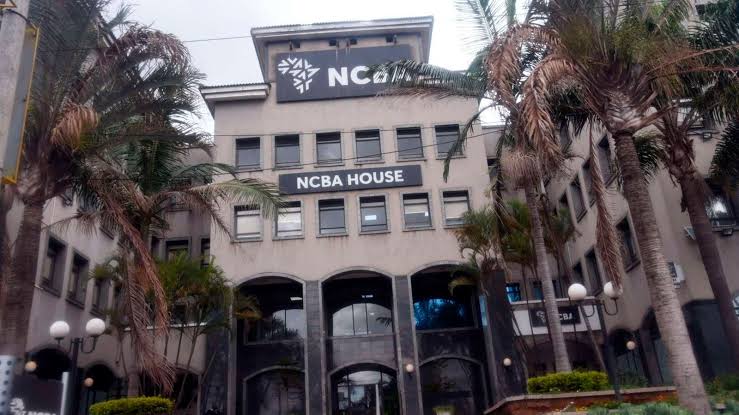
NCBA Bank has been ordered to pay Sh250,000 to a customer after it continued sharing his private business transaction details and bank statements with an unrelated person for several months, despite being notified of the error.
The ruling by the Office of the Data Protection Commissioner exposed serious failures in the bank’s handling of customer information, with the lender failing to stop the unauthorised sharing even after receiving complaints from both the affected customer and the unintended recipient.
The case involved Brian Githaiga, who opened a business account for Versilia Enterprises at NCBA in 2019. During the account registration process, the bank recorded two email addresses, one of which was incorrect and belonged to another person.
The mistake meant that the unrelated recipient continued receiving sensitive financial information, including transaction alerts and bank statements belonging to Githaiga’s business.
The unintended recipient first contacted NCBA in June 2023 to report that she was receiving financial information for an account that did not belong to her. A month later, Githaiga formally asked the bank to delete the incorrect email address from his account.
However, records presented to the data protection regulator showed that NCBA continued sending the customer’s financial information to the wrong email address until February 2024, seven months after the deletion request.
NCBA told the regulator that it had removed the email address in July 2023 but failed to explain why the private information continued reaching the unintended recipient months later.
Data Commissioner Immaculate Kassait found that the bank had negligently violated Githaiga’s right to erasure under Section 40 of the Data Protection Act, 2019.
In a determination issued in January 2025 under ODPC Complaint No. 1679 of 2024, Kassait ordered NCBA to remove the third party’s email address from the account within 14 days and compensate the customer Sh250,000.
The ruling raised questions about the bank’s internal controls and its ability to protect sensitive customer information.
The fact that both parties had reported the problem, yet the information continued being shared, pointed to a failure to properly address a known data protection breach.
The financial information involved was not ordinary correspondence. Business statements and transaction records can expose private commercial activities, making their unauthorised disclosure a serious concern for any account holder.
Reports by mid-2026 indicated that the compensation ordered by the regulator had still not been paid, raising further questions about compliance with the determination.
The case adds to previous data protection findings involving NCBA, as the regulator continues to enforce obligations requiring institutions to handle personal information responsibly.
For a bank entrusted with customers’ money and financial records, correcting an obvious error should not take months.
NCBA had an opportunity to address the problem after receiving complaints, but the regulator’s findings showed that the customer’s private financial information continued going to the wrong person.